CRACI, a Helsinki-based regtech startup, has closed a €1.4 million pre-seed round to help software companies meet the EU’s incoming Cyber Resilience Act before its first enforcement deadline hits.
The round was led by Lifeline Ventures, with participation from First Fellow Partners and Wave Ventures.


The funding arrives four months before the Cyber Resilience Act requires companies selling digital products in the EU to begin reporting actively exploited vulnerabilities and serious incidents to ENISA, the EU’s cybersecurity agency.
More than 600,000 companies worldwide, including businesses outside Europe that sell into the EU market, fall within the regulation’s scope.
CRACI was founded in 2025 by Juho Niemi, Dennis Marttinen, Jaakko Sirén, and Petteri Pulkkinen.
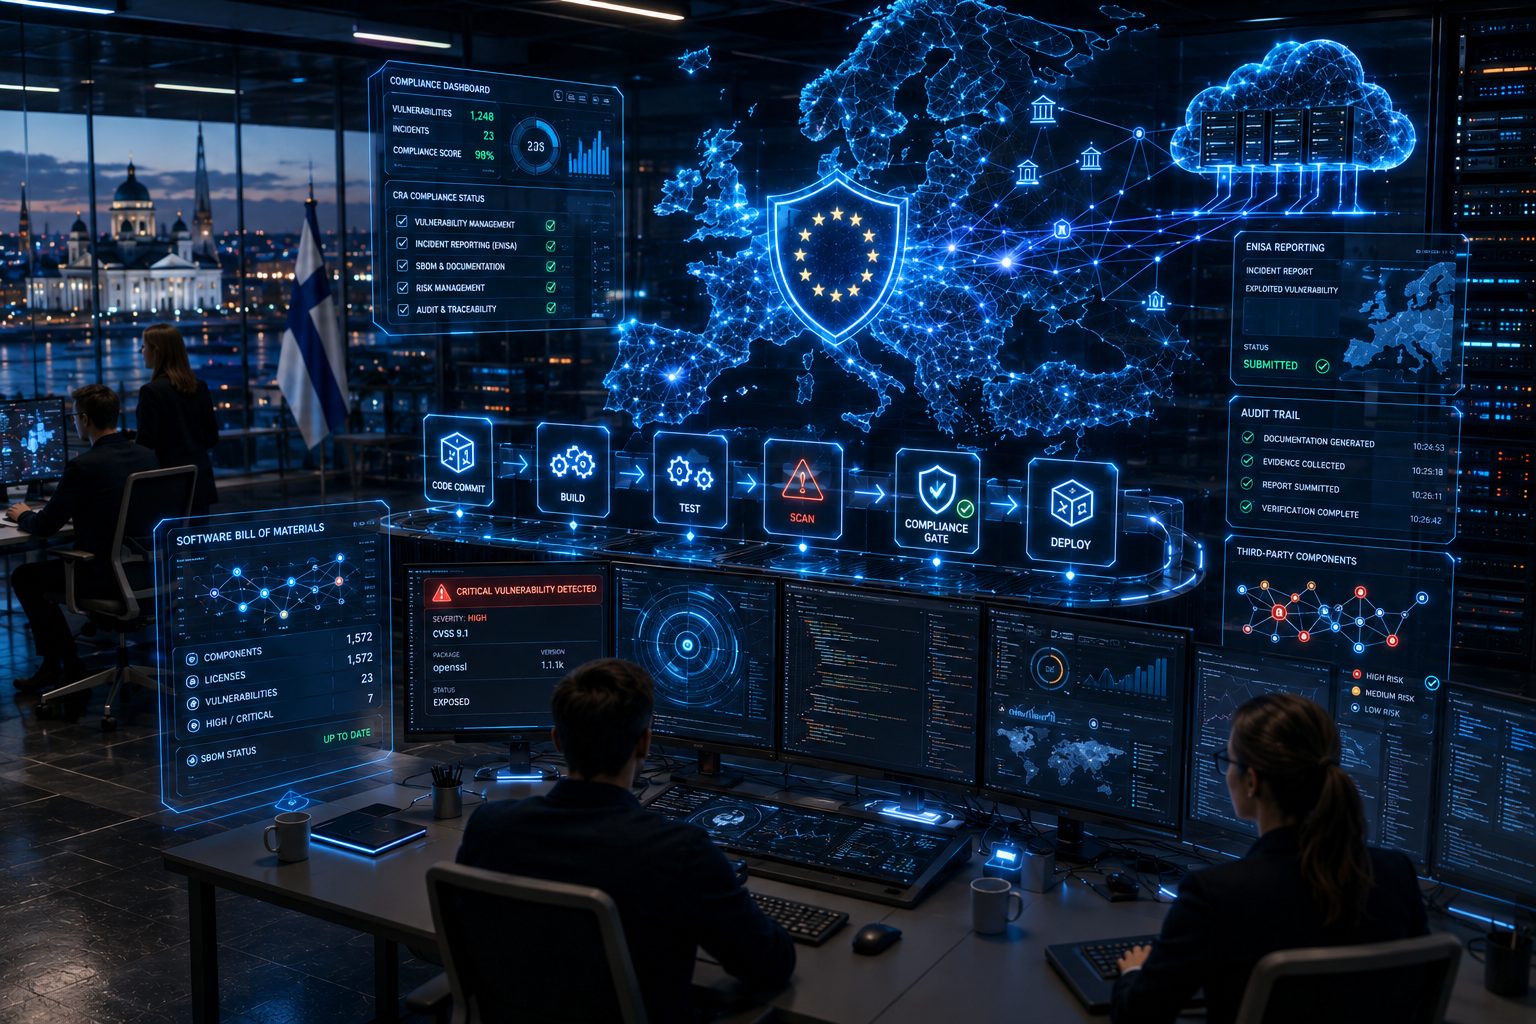
The platform plugs into a company’s existing continuous integration and delivery pipeline, tracking vulnerabilities, generating software bill of materials documentation, and archiving audit trails automatically.
The goal is to handle compliance without requiring engineering teams to maintain separate workflows.
That focus on developer experience separates CRACI from established security vendors. Tools such as Snyk, Mend.io, and Black Duck have long handled vulnerability scanning of open-source dependencies.
CRACI covers the full compliance workflow, including documentation, traceability records, and incident reporting, not just vulnerability detection.
The compliance challenge is growing more acute as software composition becomes harder to track. Third-party components, open-source libraries, and AI-generated code are expanding attack surfaces in ways that many development teams have not fully addressed.
CRACI’s automated dashboard centralizes vulnerability tracking, documentation, and ENISA reporting into one interface.
Juha Lindfors, partner at Lifeline Ventures, framed the investment in terms of the regulatory shift underway.
“The CRA is rewriting the rules for software in Europe,” Lindfors said, “and CRACI is building what this new era demands: a comprehensive compliance automation solution that fits into existing workflows.”
Lifeline Ventures is an early backer of Finnish technology companies including Wolt, Supercell, Oura, and ICEYE.
The firm focuses on pre-seed and seed investments, often entering before a product is complete.
Its involvement signals confidence that compliance automation for the CRA represents a durable market, not a short-cycle regulatory trade.
The proceeds will go toward product development and engineering hires as CRACI prepares for the September 2026 enforcement date.
How the CRA Deadline Structure Affects Software Sellers
The regulation’s obligations arrive in phases. The first hard date is September 11, 2026, when manufacturers must begin reporting exploited vulnerabilities and severe incidents to ENISA.
Full applicability follows on December 11, 2027, covering broader security, documentation, and lifecycle management standards for all products with digital elements sold in the EU.
Non-compliance carries fines of up to €15 million, or up to 2.5 percent of global annual turnover, whichever is higher.
Companies that cannot demonstrate compliance face losing market access across the bloc.
The Finnish Government submitted its national CRA implementation proposal to Parliament on November 27, 2025, designating the Finnish Transport and Communications Agency Traficom as the main supervisory authority.
Firm Dates Ahead for Companies in Scope
- September 11, 2026: ENISA incident and vulnerability reporting begins under the CRA.
- December 11, 2027: Full CRA obligations apply to all products with digital elements sold in the EU.
June 1, 2026: Finland’s national supplementary CRA law is set to enter into force.